01
Server-side, without a CDN migration
Use BotDetect from your existing stack. Core detection does not require browser JavaScript, a DNS move or putting your application behind another reverse proxy.
BotDetect is a server-side bot intelligence API for websites and applications. Send request metadata and receive an explainable 0–10 score, reason, signals and recommendation — without moving your traffic behind another CDN or giving up control of enforcement.
{
  "request_id": "req_7H2K",
  "score": 9,
  "reason": "fakecrawler",
  "action": "block",
  "signals": [
    "googlebot_asn_mismatch",
    "browser_headers_missing",
    "ip_reputation"
  ]
}BotDetect separates detection from enforcement. Your backend sends request context, BotDetect evaluates it in real time, and your application decides whether to allow, monitor, challenge or block.
Use BotDetect from your existing stack. Core detection does not require browser JavaScript, a DNS move or putting your application behind another reverse proxy.
Receive a 0–10 score together with a reason and concrete signals. Understand why a request looks suspicious instead of relying on an opaque yes/no decision.
Benefit from shared reputation created from abusive behavior observed across BotDetect nodes and participating customers. Reputation is a signal — not an automatic permanent block.
BotDetect recommends an action, but your application owns the final decision. Start in monitor mode, inspect the data and enforce only where it makes sense.
Plugin, PHP client or REST integration sends request metadata before expensive application work.
A regional BotDetect node evaluates headers, crawler identity, ASN, behavior and shared reputation.
Your application receives the explanation and decides whether to allow, monitor, challenge or block.
Unwanted requests consume bandwidth, PHP workers, application CPU, database time, logs, cache capacity and sometimes paid third-party APIs. Tiny per-request costs become real infrastructure spend at scale.
Reject suspicious traffic before it reaches expensive application logic whenever your architecture allows it.
Identify automated crawlers and decide whether they should be monitored, challenged or blocked.
Detect clients claiming to be legitimate search crawlers when their network identity and behavior do not match.
If one unwanted request costs only €0.0001 in origin compute, bandwidth, database work and logging, the cost grows quickly.
Illustrative example only. Actual infrastructure cost per request depends on your application, hosting model, caching and where BotDetect is integrated.
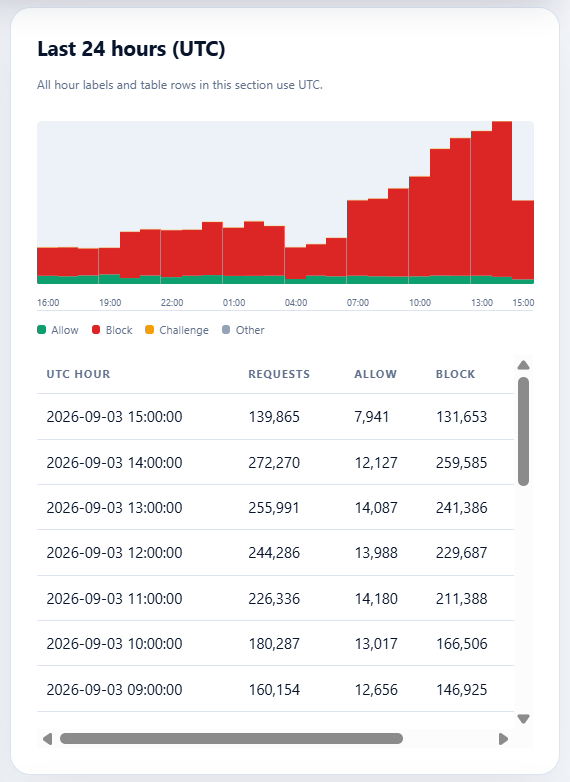
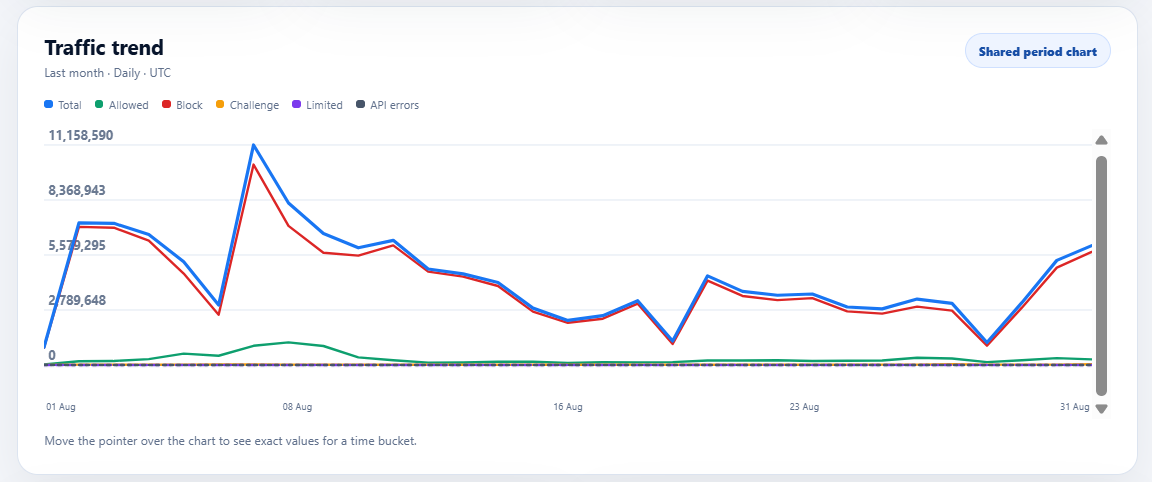
The more than 147 million figure is the total request volume processed by BotDetect during the last month. The screenshots below are selected traffic statistics from the dashboard of a real BotDetect customer and show what an individual customer can see in their own dashboard.
Start with a WordPress plugin, call the REST API directly or use shared reputation as an additional security signal in higher-volume environments.
Protect frontend pages, wp-login.php, XML-RPC, REST API and admin-ajax. Monitor first, see how much traffic is automated, then enable challenge or block modes when you are comfortable.
Call BotDetect over HTTPS from any backend stack. Receive score, reason, signals and recommendation while keeping your own application logic and enforcement.
API workflowUse the ready-to-use PHP integration from custom applications and common PHP frameworks without introducing client-side fingerprinting as a requirement.
Server-side workflowPremium environments can use shared reputation built from observed abuse as an additional signal beyond individual request scoring.
Ask about reputation accessBlocking is only one outcome. BotDetect helps site owners understand which parts of WordPress attract automation, test protection in monitor mode and reduce unnecessary application work before turning on enforcement.
Plans are shown as approximate 30-day request capacity. Technical hourly limits remain in place to protect service stability and keep traffic bursts predictable.
€0/month
≈720K requests/month
For testing BotDetect on one website.
€35/month
≈28.8 million requests/month
For production websites with steady traffic.
€100/month
≈86.4 million requests/month
For the same Standard features with higher request capacity.
Custom
Custom request capacity
For high-volume environments and reputation intelligence use cases.
Monthly figures are 30-day equivalents of each plan's technical hourly capacity. Limits are enforced hourly; unused hourly capacity does not roll over into another hour.
BotDetect is an independently developed and operated EU-based security service. The project focuses on direct technical ownership, minimal data use and infrastructure controls that are appropriate for a security product.
Customer account, service configuration and central control-plane data are managed from EU-based infrastructure. Request metadata is evaluated by geographically distributed BotDetect API nodes to keep scoring latency low.
Payment processing is delegated to PayPal. BotDetect does not need to store customer card numbers or process raw card details itself.
BotDetect does not sell customer data or share it for advertising. Operational data is used to provide the service, protect it, build security reputation and support customers.
Hosts and software are kept updated, public exposure is minimized, TLS is used for service traffic, application secrets are separated from public code and internal data services are not intentionally exposed to the Internet.
The service is currently developed and operated directly by its owner. Technical questions and security issues do not disappear into a multi-layer support chain — they reach the person responsible for the architecture and operations.
Need an architecture review, data-processing explanation or security questionnaire answered before deployment? Contact the project directly and get a technical response rather than generic sales copy.
BotDetect makes only the security and compliance claims it can substantiate. Formal certifications are not implied by this page.
BotDetect is designed around one simple idea: you should be able to add bot intelligence to an existing application without moving your traffic behind a new CDN or surrendering enforcement control.
The system combines request-level analysis with crawler verification, behavioral signals and shared reputation. Detection remains explainable, while your application decides what happens next.
Being independently operated keeps the feedback loop short: product development, infrastructure decisions and technical support are connected directly.
Connect your first site, observe real decisions and use BotDetect as an intelligence layer before enabling enforcement.